

OneNAC
Network Access Control
The OneNAC access gateway combines authentication, security checks, remediation, access control, and behavior auditing. It helps meet core business access-control and network-compliance requirements through identity management for users and devices, network-boundary protection, and endpoint discovery, location, traceability, and auditing.
OneNAC combines authentication, security checks, access control and auditing to identify users and devices, protect network access and trace activity.
Network Access Control
Control Critical Resource Access and Secure Network Boundaries
OneNAC helps control access to core business systems and meet network security requirements. It verifies user and device identities, protects network boundaries, and supports endpoint discovery, location, traceability, and auditing.
Explore Now

Compatibility
Supports multiple mainstream network access technologies and allows different blocking methods to run in parallel, avoiding the limits of relying on a single technology in a given environment.

Extensibility
Beyond core network access control, endpoint security management features can be added seamlessly to keep connected devices secure and trusted.

Flexibility
Pure bypass deployment requires no changes to network structure or configuration. Multiple disaster-recovery options help ensure high reliability.
Network Admission Security and Access Control
Control device access to help prevent risks from unauthorized connections, including virus spread, data leaks, malicious attacks, Trojan installation, and covert monitoring.
Endpoint Access
Meet different enterprise network-access requirements with flexible options, including identity authentication, client installation, and administrator approval.
Access Inspection
Set custom compliance checks to isolate risky endpoints and remediate them automatically, so devices meet the security baseline before connecting.
Network Assets
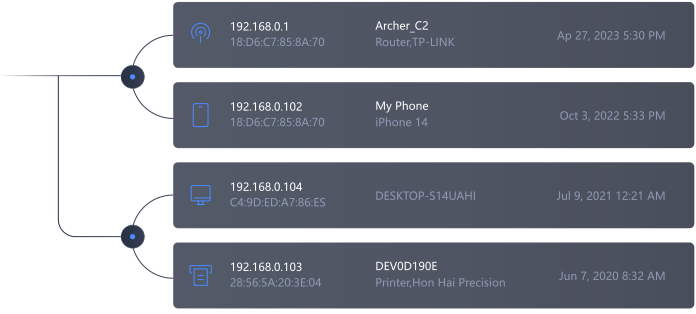
Use active scanning and passive network monitoring to discover connected devices, identify their types, and display them visually.
Identity Authentication
Support local accounts, Active Directory, SMS, and other authentication methods for verified user identities and centralized access management.
Network Management
Keep audit records for connected devices and manage IP addresses throughout their lifecycle in a unified secure-access platform.
Visitor Management
Provide flexible, purpose-built authentication and access management for visitors to support a complete network-admission process.
Application Scenarios
Guest Access Network
Scenario Description
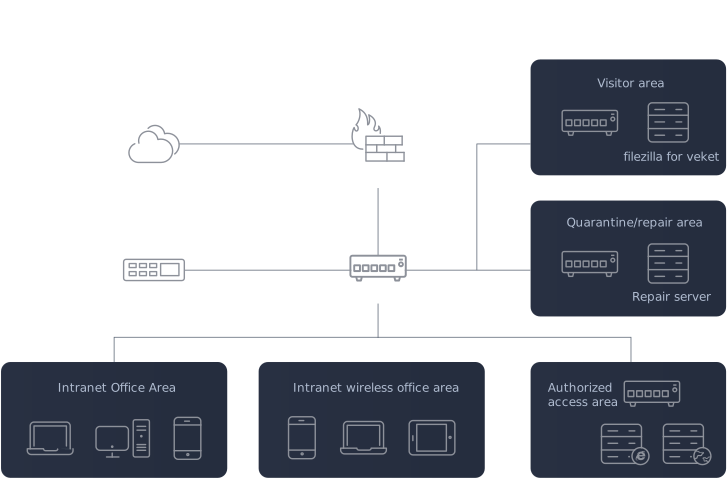
As partner visits become more common, visitors may connect to the network and access internal resources without adequate controls. Their devices may also lack verified security, creating risks for the internal network.
Problems Addressed
● Standardize the visitor network-access process
● Prevent internal data leaks
● Identify and locate visitor devices
● Prevent unauthorized access
Internal Network Access Compliance Management
Scenario Description
As the internal network grows and endpoint types multiply, inconsistent security settings make centralized management difficult for IT teams. When an incident occurs, they may also struggle to locate it and respond quickly.
Problems Addressed
● Centralize asset management
● Define and deploy endpoint security policies consistently
● Link people to their devices
● Locate and audit security incidents
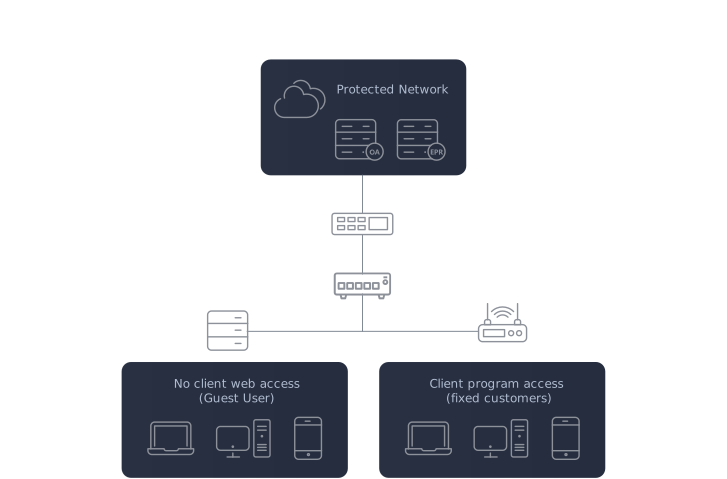
Solution value

Centralized Device Access Management
The system provides end-to-end network access control, from device discovery and visitor management to authentication and authorization, compliance checks, isolation and remediation, permissions, and access traceability.

Flexible Authentication and Access Control
Flexible, easy-to-use hybrid access controls support graded protection requirements and help organizations make network access visible, keep devices trusted, and control network boundaries.

Meet Security Compliance Requirements
Detect unauthorized devices connected to the internal network, locate them automatically and visually, and control their access to network resources.

Integrated, Secure, and Controlled Operations
Integrate with Ping32 endpoint security management to enforce compliant device access, standardize internal network management, and reduce security gaps.
Start using OneNAC right away
Contact us to discuss your requirements and a deployment plan for your organization.


